Snyk AI
Snyk / snyk.io
AI-powered developer security platform for finding and fixing vulnerabilities in code, open source dependencies, containers, and infrastructure as code directly in developer workflows.
Pricing
$25/mo
Free plan
Yes
Category
Developer Tools
Platforms
7
Free plan
Yes
API access
Yes
Open source
No
Platforms
7
Advertisement
What is Snyk AI?
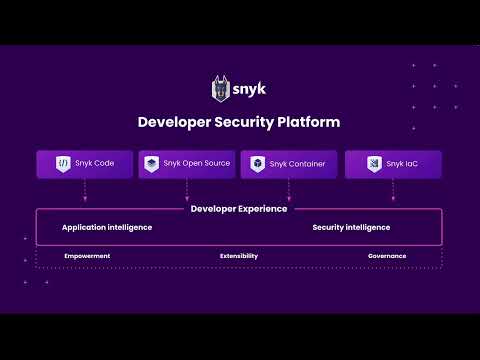
Snyk is a developer-first security platform that finds and fixes vulnerabilities in application code, open source dependencies, container images, and infrastructure as code, integrated into the developer workflow tools teams already use rather than requiring developers to switch to a separate security interface.
Snyk Open Source scans project dependencies against Snyk's curated vulnerability database, which is one of the largest commercial vulnerability databases with additional intelligence beyond the public National Vulnerability Database (NVD). The fix recommendations suggest specific version upgrades that resolve vulnerabilities with the least breaking change impact.
Snyk Code performs static application security testing (SAST) with AI-powered analysis that understands code semantics rather than only pattern matching, reducing the false positive rate that makes traditional SAST tools painful to use. DeepCode AI, acquired by Snyk, provides the AI foundation for this semantic code analysis.
Snyk AI features include AI-generated fix suggestions that provide actual code patches for found vulnerabilities rather than only flagging issues. For developers who want to fix a vulnerability, Snyk can suggest the code change needed rather than leaving the developer to research the fix independently.
At $25/user/month for Team, Snyk is accessible for development teams that want to integrate security earlier in the development lifecycle without waiting for dedicated security team reviews.
How Snyk AI works
Snyk AI runs as document analysis llm software built around code and text workflows. Users typically start with a prompt, upload, or connected data source, and the underlying model handles the heavy lifting before returning a result you can refine or export. It's available on vs code, intellij, and github, with API access for teams that want to embed it into their own products.
Watch Snyk AI in action
Recent YouTube videos cached from the backend so this page stays fast and fresh.
What makes it worth shortlisting
The capabilities that matter most for teams evaluating Snyk AI.
Snyk Open Source
Scans project dependencies against Snyk's curated vulnerability database to identify known vulnerabilities in open source libraries with specific version fix recommendations.
Snyk Code
AI-powered semantic SAST that understands code logic and data flows, reducing false positive rates compared to traditional pattern-matching SAST tools.
AI-generated fix suggestions
Provides actual code patches for found vulnerabilities rather than only describing issues, reducing the time from detection to fix for development teams.
Best use cases
Who should use it
Pros
- Developer-first design means security integrates into existing workflows without context switching
- AI-generated fix suggestions provide actual code patches rather than just issue descriptions
- DeepCode AI semantic analysis reduces false positives that make traditional SAST tools painful
- Free plan allows meaningful evaluation of open source dependency scanning
Cons
- Team plan at $25/user/month adds up quickly for large engineering teams
- AI fix suggestions require developer review — not all suggested fixes are appropriate for every context
- Some scanning requires transmitting code to Snyk's infrastructure — review for sensitive codebases
Advertisement
Is it worth the price?
Free plan (10 tests/month). Team $25/user/month. Business $62/user/month. Enterprise custom. Monthly or annual billing.
Model
Freemium
Starting price
$25/mo
Free trial
No
Tools like Snyk AI
GitHub Advanced Security is a competing integrated security platform for GitHub users. Checkmarx and Veracode are traditional enterprise SAST competitors. Wiz focuses on cloud infrastructure security. SonarQube focuses on code quality alongside security.
Snyk AI vs Veracode AI
A side-by-side look at the closest alternative in this category.
Snyk AI
Snyk
Veracode AI
Veracode
Free plan (10 tests/month). Team $25/user/month. Business $62/user/month. Enterprise custom. Monthly or annual billing.
Enterprise licensing. No public pricing. Annual contracts. Privately held (Broadcom subsidiary). Demo available.
SOC 2 Type II. ISO 27001. GDPR compliant. FedRAMP authorised. Code scanning processes code on Snyk's infrastructure or locally depending on deployment.
SOC 2 Type II. ISO 27001. GDPR compliant. FedRAMP authorised. Enterprise data handling agreements.
Snyk Code can be run locally (local scanning engine option) keeping code on developer infrastructure. Open source scanning metadata transmitted to Snyk. Review data handling for proprietary code scanning use cases.
Source code and binary application data transmitted to Veracode cloud for analysis. FedRAMP for US government application security scanning.
- Developer-first design means security integrates into existing workflows without context switching
- AI-generated fix suggestions provide actual code patches rather than just issue descriptions
- DeepCode AI semantic analysis reduces false positives that make traditional SAST tools painful
- Free plan allows meaningful evaluation of open source dependency scanning
- Adobe, IBM, and Expedia validate Veracode for enterprise application security at major software scale
- Veracode Fix AI-generated code patches reduce time from vulnerability identification to remediation
- Binary analysis uniquely enables scanning third-party and legacy applications without source code access
- FedRAMP authorisation enables US government application security scanning
- Team plan at $25/user/month adds up quickly for large engineering teams
- AI fix suggestions require developer review — not all suggested fixes are appropriate for every context
- Some scanning requires transmitting code to Snyk's infrastructure — review for sensitive codebases
- Broadcom subsidiary — evaluate product investment continuity under semiconductor company ownership
- Transmitting code to cloud for scanning may concern organisations with strict IP protection requirements
- Competing with Checkmarx (rank 812), Snyk (covered), and GitHub Advanced Security for AST market
Technical & deployment info
Key facts about model providers, platforms, and team support.
Model Provider
Snyk, DeepCode
Platforms
VS Code, IntelliJ, GitHub, GitLab, Bitbucket, CLI, CI/CD
Deployment
SaaS
Integrations
GitHub, GitLab, Bitbucket, Jenkins, CircleCI, AWS CodePipeline, Jira, Slack
Team Collaboration
No
Launch Year
2022
Security & privacy
Compliance signals and data-handling notes as reported by the vendor.
SOC 2 Type II. ISO 27001. GDPR compliant. FedRAMP authorised. Code scanning processes code on Snyk's infrastructure or locally depending on deployment.
Snyk Code can be run locally (local scanning engine option) keeping code on developer infrastructure. Open source scanning metadata transmitted to Snyk. Review data handling for proprietary code scanning use cases.
What users are saying
Verified reviews from signed-in users, stored in the backend and averaged into this tool's rating.
Sign in to rate Snyk AI and leave a review.
No other reviews yet — be the first to share how this tool performs in practice.
Common questions about Snyk AI
Editorial Verdict
Should you use Snyk AI?
Snyk is the best AI developer security platform for engineering teams who want security integrated into their existing developer workflow without requiring a separate security team process.
Last verified July 24, 2026.